DDoS protection
Monitoring & mitigation
Continuous monitoring, Flowspec mitigation and upstream GRE scrubbing. Our engineering team helps plan and adjust protection based on traffic characteristics and the impact of an incident.
 Technical illustration · not a company equipment photo
Detection & mitigation
Detection in < 10s, Flowspec rules deployed in < 15s. BGP sessions stay up during attacks, legitimate traffic unaffected.
Inspect traffic. Choose the mitigation path.
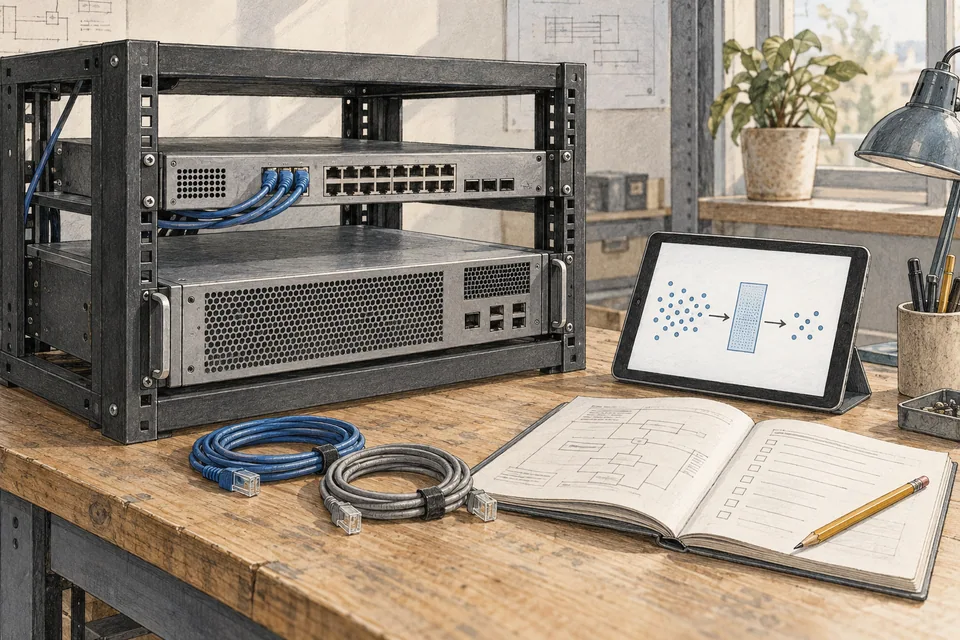 Technical illustration · not a company equipment photo
Compare the traffic baseline and attack signature, then select filtering or scrubbing. Engineers review and adjust the response.
24×7 · NOCMitigation process
Baseline comparison, signature ID.
Attack type, source, target classified.
Flowspec rules issued, GRE scrubbing on.
Full analysis report within 24h.
Protection options
Traffic baselines, attack characteristics and mitigation records are available to support investigation and future adjustments.
24×7 traffic baselining, automated anomaly detection — < 10s attack signature ID.
BGP Flowspec rules issued automatically per signature — legit traffic preserved.
Upstream scrubbing centres via GRE tunnel, clean traffic returned via original path.
BGP sessions stay up during attacks — your network remains reachable throughout.
SYN flood, UDP flood, ICMP flood, amplification — full L3/L4 coverage.
Detailed post-incident analysis within 24h: signature, mitigation timeline, traffic.
Attack coverage
Forged TCP SYN flood, exhausting connection state
High-volume UDP saturation of bandwidth
DNS / NTP / Memcached reflection amplification
L7 application-layer high-rate requests
Ping of Death / high-rate ICMP
Slow connections exhausting workers
Ongoing engineering support
24×7 NOC, rotating between Tokyo and Taipei. Flowspec rules engineer-reviewed before deployment — no single point of automation.
An alert arrives. Engineers take over.
 Illustrated work scene · not a staff photo
- 01 / OBSERVE
- Alerts and traffic
- Understand the impact
- 02 / INVESTIGATE
- Routes and runbooks
- Check anomalies and response steps
- 03 / RESPOND
- Review and coordinate
- Rule review · incident communication
Plan DDoS protection
Tell us your service type (Web / API / Gaming / VoIP), expected peak, and prior attack scale — we will respond within one business day.